
DocsPeople and access
Least privilege
Compare what each identity may do with what it actually did, and narrow it in a plan you confirm, with undo.
Least privilege (admins) compares what each identity may do with what it actually did in the last 90 days, and proposes exactly that.
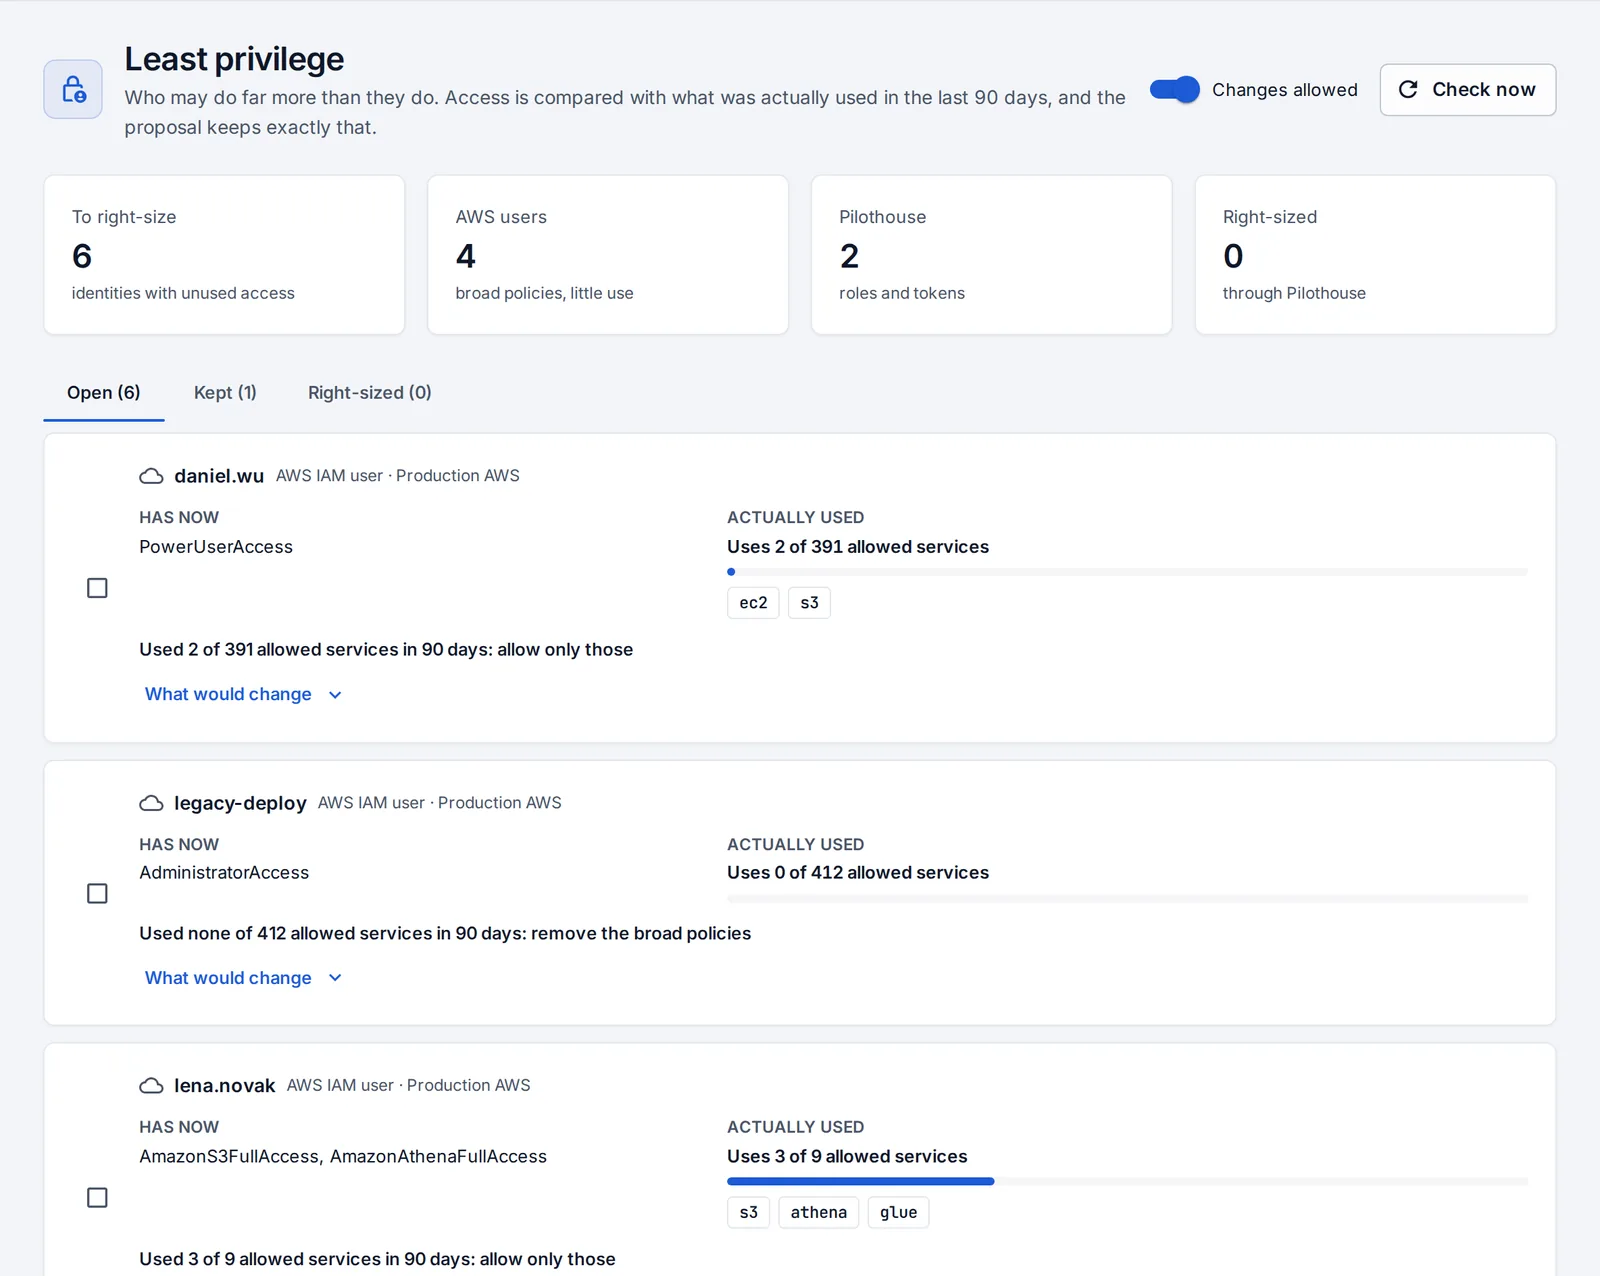
AWS IAM users
For users with broad policies attached (AdministratorAccess, PowerUserAccess, IAMFullAccess, any *FullAccess), IAM’s own “last accessed” report says which services they used. The proposal is one inline policy allowing only those services, replacing the broad ones. A user who used nothing just loses them.
Broad access that comes from a group is only reported: changing a group changes everyone in it.
OpsNexa Online accounts and tokens
From the audit log:
- an admin who used no admin-only feature can be a developer (or a tester, if they changed nothing);
- a developer who changed nothing can be a tester;
- a full-access token that never changed anything can be read-only, and a token nobody used can be revoked.
The last admin is never demoted.
Making changes
It starts review only. An admin turns on Changes allowed, then right-sizes through a plan they confirm:
- for AWS, the narrow policy is added before the broad ones are detached, so there’s no moment without the access that’s actually used;
- Undo puts everything back.
Keep as is (with a reason) is for access used rarely, like a yearly export or a break-glass admin.
Something unclear or missing? Tell us, or press the ? at the top of OpsNexa Online for the guide and tours inside the product.